Security
GxPAccess Control & Security
The right people, the right documents — and no one else.
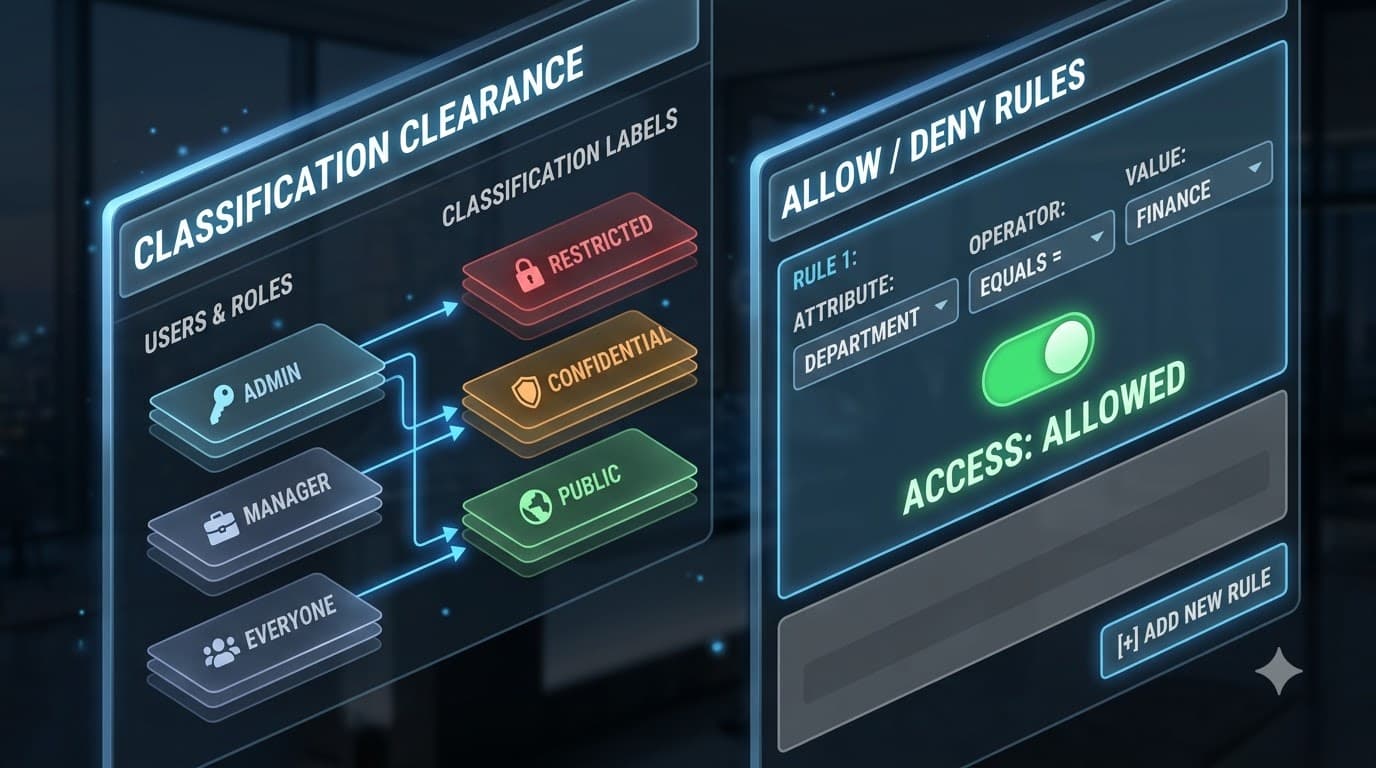
Fine-grained permissions gate every action, and attribute-based rules (deny wins) scope access by security class, category, project, department and plant. Documents are classified public → restricted, and clearances decide who can open what.
What you get
Built to hold up under scrutiny
Attribute-based access
Allow/deny rules by subject and document dimension — security class, category, project, department, plant — with deny-wins precedence.
Classifications & clearances
Documents are public / internal / confidential / restricted; users and roles carry a maximum clearance.
Multi-tenant & plant-scoped
Each tenant is isolated at the schema level, and access is plant-aware for multi-site organizations.
Capabilities
Inside this capability
- Granular permission strings on every route
- Attribute-based allow/deny rules with deny-wins precedence
- Security classification (public → restricted) driving confidentiality watermarks
- Per-user and per-role maximum clearance levels
- Plant-aware access, distribution and repository grouping
- Multi-tenant schema isolation
How it flows
Step by step
- 1
Classify
A document gets a security class and its plant / department dimensions.
- 2
Resolve rules
Access is evaluated against allow/deny rules, deny winning ties.
- 3
Check clearance
The user’s maximum clearance must meet the document’s class.
- 4
Gate
Only cleared users can open, print or receive a controlled copy.
FAQ
Access & security — questions
Deny always wins. Access is granted only when an allow rule matches and no deny rule does, evaluated across subject and document dimensions.
Yes. Each organization is isolated at the database-schema level, and access, distribution and the repository tree are all plant-aware for multi-site operations.
Ready to put your documents on the record?
See how YourDocVault controls the full lifecycle — with the audit trail, e-signatures and controlled copies your quality system needs.