Part 11
GxP21 CFR Part 11 E-Signatures
Signatures that stand up to an auditor.
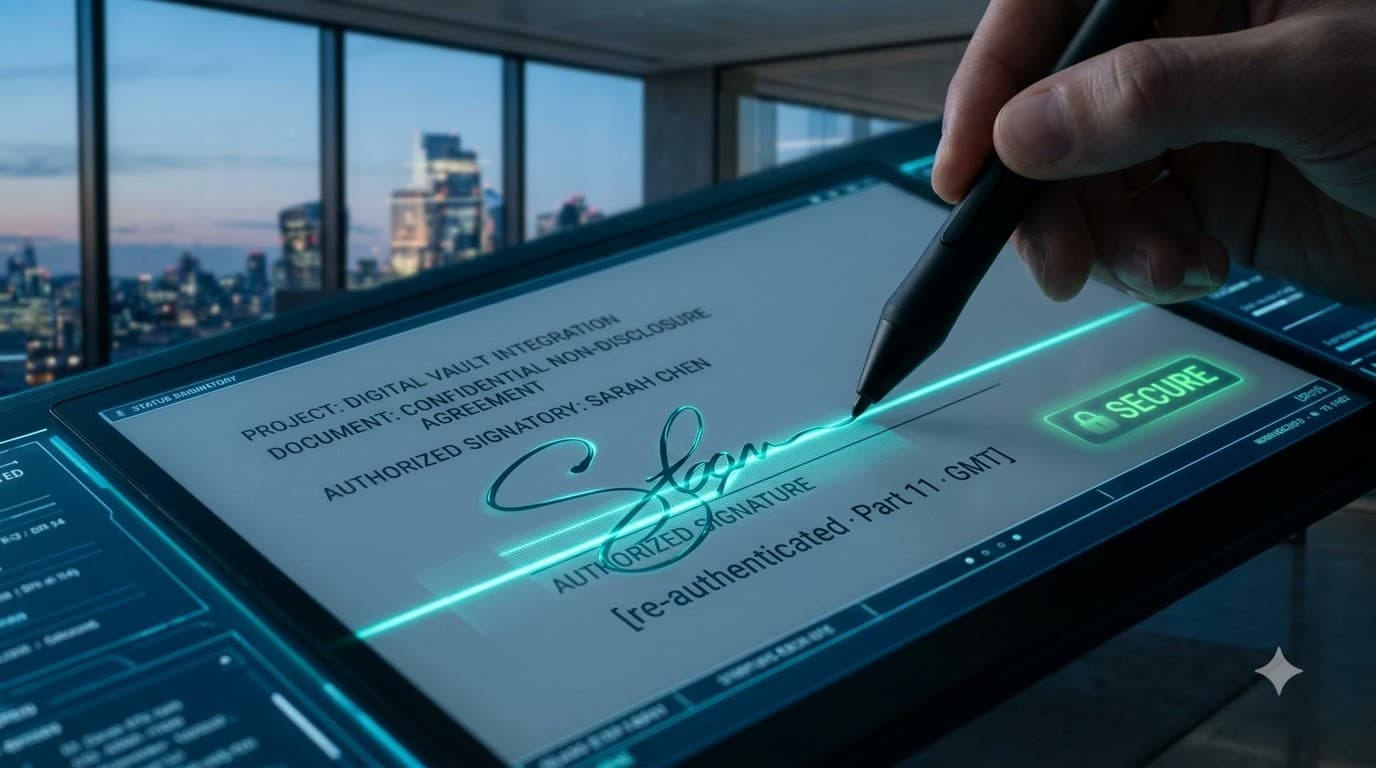
Electronic signatures are append-only, hash-sealed records capturing the signer, the meaning, the authentication method and a GMT timestamp — and they can’t be edited or deleted. Signing requires a fresh, contemporaneous re-authentication.
What you get
Built to hold up under scrutiny
Signer re-authentication
Every signature demands a fresh credential / MFA re-auth against the identity service before it commits.
Meaning on every signature
Each record carries the reason for signing — authored, reviewed, approved — bound to the exact action.
Signature placement
Approvers drag their signature image onto any page of a .docx or PDF; each placement is a retained, e-signed revision.
Capabilities
Inside this capability
- Append-only, DB-trigger hash-sealed e-signature records — never updatable or deletable
- Contemporaneous signer re-authentication for a unique signature per action
- Configurable per-tenant, per-feature, per-action signature policies
- Actions covered: create, update, submit, review, acknowledge, retire, dispose, legal-hold
- Signature placement embedded in DOCX or stamped onto PDFs
- Signature manifest listing every collaborator and stage — name, title, GMT time, meaning
- Each signature linked to its audit-trail record
How it flows
Step by step
- 1
Act
A user submits, reviews or approves an action that policy marks as signature-required.
- 2
Re-authenticate
They re-enter credentials / MFA — a fresh, contemporaneous authentication.
- 3
Seal
The signature is written append-only and hash-sealed with its meaning and GMT time.
- 4
Manifest
The composed signature manifest reflects every signer, sourced from the records.
FAQ
E-signatures — questions
YourDocVault is built to support Part 11 electronic-signature controls: unique, re-authenticated, contemporaneous signatures that record signer, meaning and time, held in an append-only, hash-sealed store. Final compliance always depends on your validated deployment and procedures.
No. The signature table is append-only and hash-sealed by a database trigger — records cannot be updated or deleted.
Ready to put your documents on the record?
See how YourDocVault controls the full lifecycle — with the audit trail, e-signatures and controlled copies your quality system needs.