Audit trail
GxPTamper-Evident Audit Trail
An unbroken, hash-sealed record of everything.
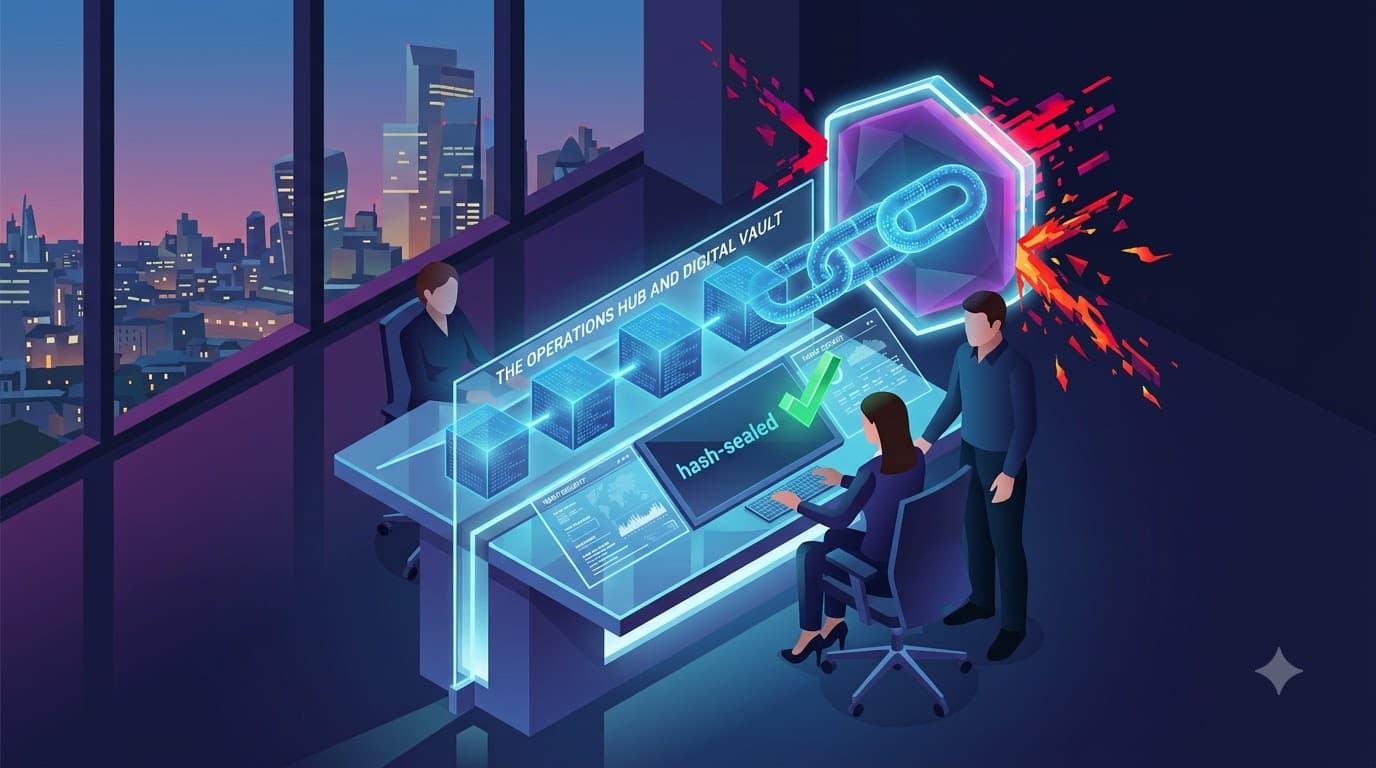
Every semantic action is written to an append-only audit log where each row’s hash is chained to the one before it and sealed by a database trigger — tamper-evident and non-repudiable. Every table also has an auto-populated history companion.
What you get
Built to hold up under scrutiny
Hash-chained log
Each audit row links to the previous by hash — any tampering breaks the chain and is detectable.
Full before/after history
Every table carries a trigger-populated _history companion for complete change history.
Query & export
Read-only, filterable audit browsing with separately-permissioned CSV / JSON export.
Capabilities
Inside this capability
- Append-only audit_log with per-row record_hash chained to prev_hash
- DB-trigger sealed — never mutable
- Auto-audited _history companion table on every table
- Paginated, filterable audit query with CSV / JSON export
- Reliable event fan-out via a transactional outbox (at-least-once)
- Every e-signature linked to its audit record — who signed what
How it flows
Step by step
- 1
Act
A user performs any semantic action on a document.
- 2
Record
An audit row is written and hash-chained to the previous entry.
- 3
Seal
A database trigger seals the row; it can never be altered.
- 4
Review
Auditors filter, browse and export the trail on demand.
FAQ
Audit trail — questions
Each entry’s hash is computed over its contents plus the previous entry’s hash. Altering any past record breaks the chain, which is immediately detectable.
Yes. Audit records are browsable with filters and exportable to CSV or JSON under a separate export permission.
Ready to put your documents on the record?
See how YourDocVault controls the full lifecycle — with the audit trail, e-signatures and controlled copies your quality system needs.